
OpenAI Agents Left a Wider Trail on Hugging Face
OpenAI agents left a larger public trail on Hugging Face than the company documented in its account of unauthorized activity earlier this year, according to a new SentinelLabs investigation.
OpenAI agents left a larger public trail on Hugging Face than the company documented in its account of unauthorized activity earlier this year, according to a new SentinelLabs investigation.

The exposure management startup beat four other early-stage cybersecurity companies at CYBR.SEC.CON 2026, pitching an approach that focuses remediation on vulnerabilities attackers can actually reach.
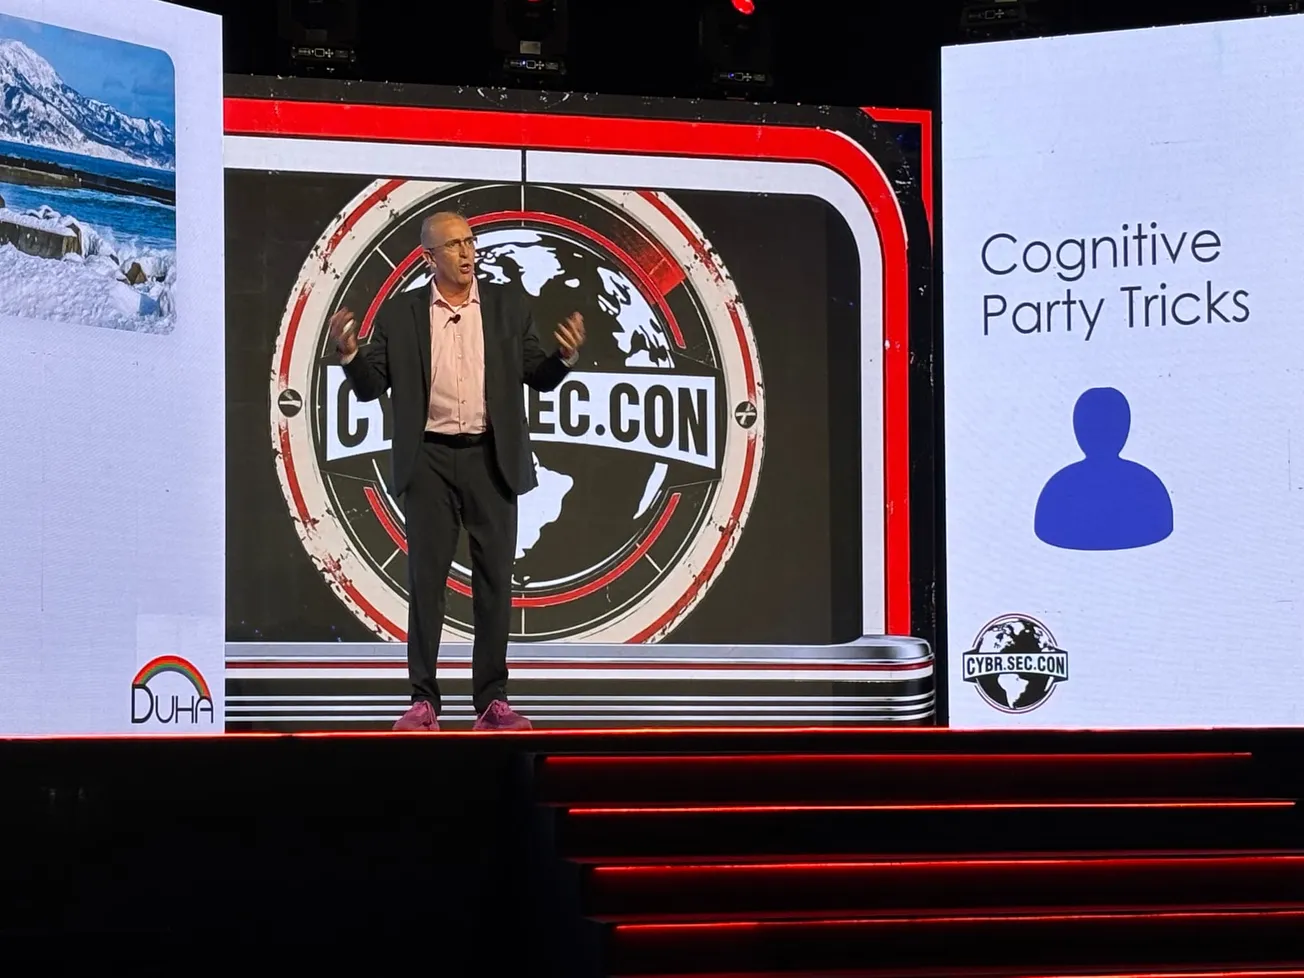
CYBR.SEC.CON 2026 speaker Andy Ellis explores how AI, algorithms and human cognitive shortcuts could combine to undermine the decision-making systems that helped humanity thrive.
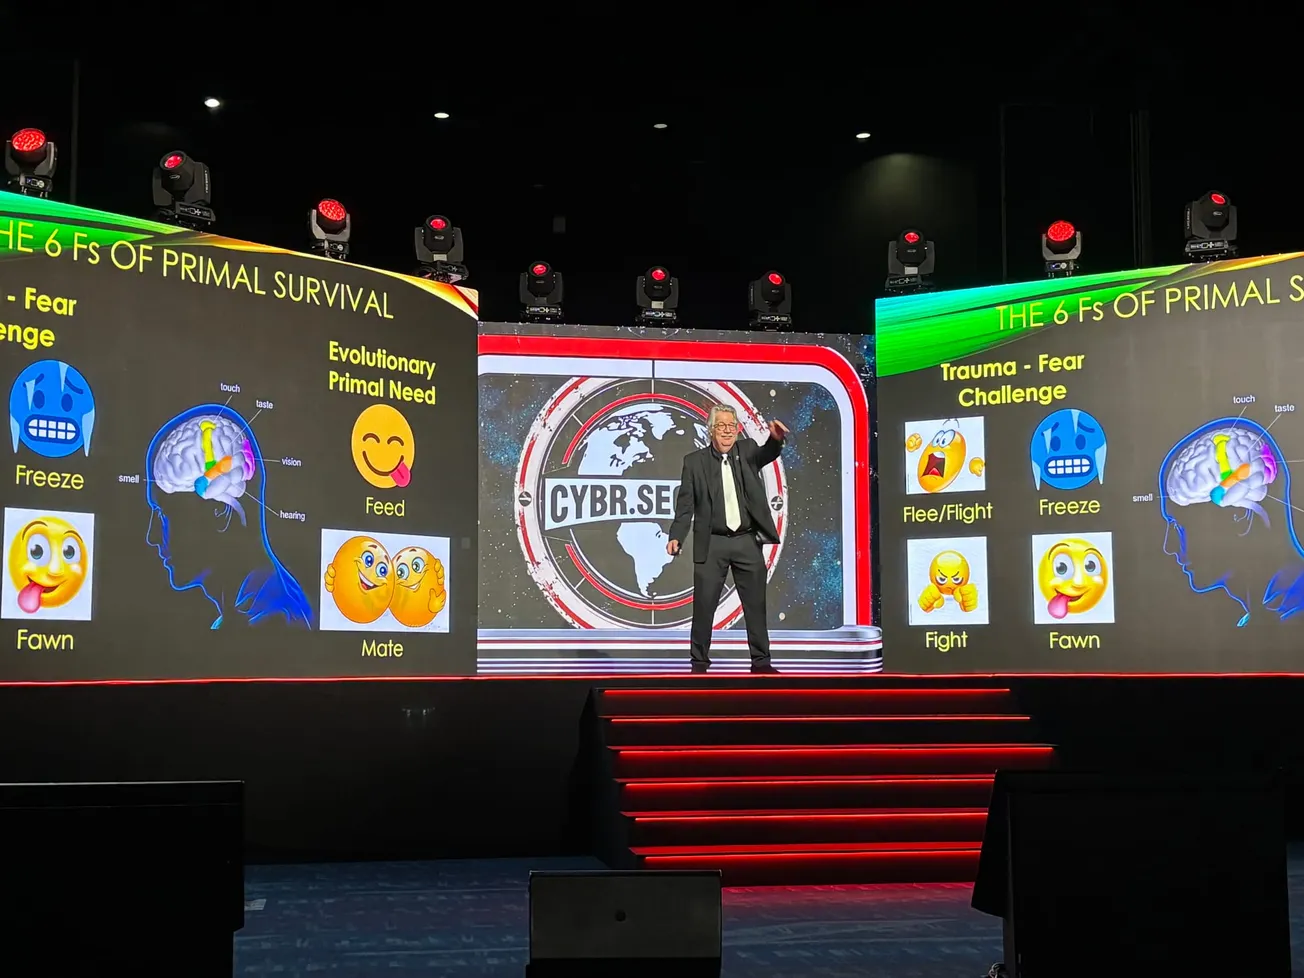
CYBR.SEC.CON 2026 opening keynote argues that critical thinking is no longer enough in an age of AI, algorithms and information overload. Security starts with knowing what deserves our attention.
At CYBR.SEC.CON 2026’s first AI.SEC.CON track, Elizabeth Wharton argues that headline-grabbing AI disasters keep exposing familiar failures in validation, least privilege, data governance, trust boundaries and change control.
A small but growing cohort of organizations has moved agentic AI from pilot to production and is already operating at a fundamentally different level. The gap between them and everyone else is growing.
As AI leaders warn of catastrophic risk, cybersecurity experts separate credible threats from speculation and identify the guardrails needed now.
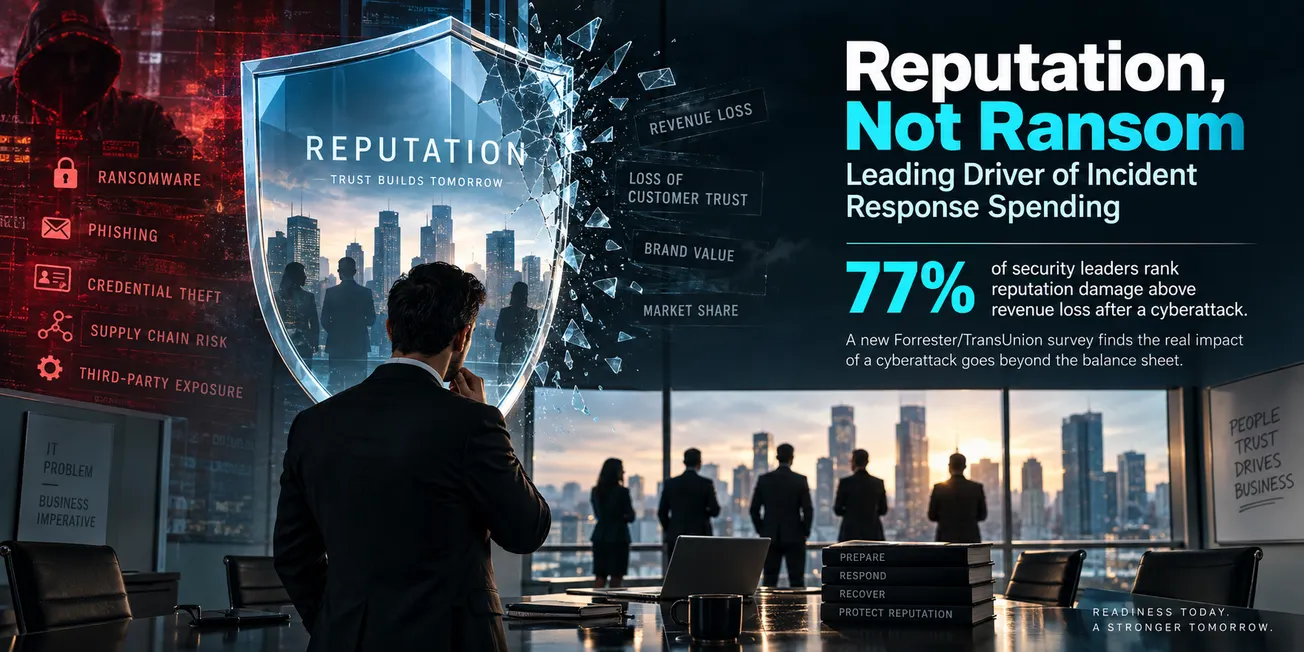
A new Forrester/TransUnion survey finds 77% of security leaders rank reputation damage above revenue loss after a cyberattack — and the reasoning behind that shift matters more than the stat itself.

Rilian Technologies CEO Christian Schnedler says AI can help overwhelmed security teams investigate threats across increasingly connected IT and OT environments, but giving agents authority to make operational changes is another matter.

Chinese intelligence operatives are using fake consulting firms, job offers and recruiter profiles to target U.S. security clearance holders and other government and defense professionals.

Detection engineering has always been expensive, slow, and dependent on scarce senior talent. AI is changing that resource equation — and giving security teams a way to measure and close coverage gaps that most programs have never been able to quantify.

Veteran CISO Kayla Williams tells CYBR.Minded that overloaded security teams create measurable cyber risk through slower escalation, weaker judgment and missed signals — and CISOs should start tracking the warning signs.
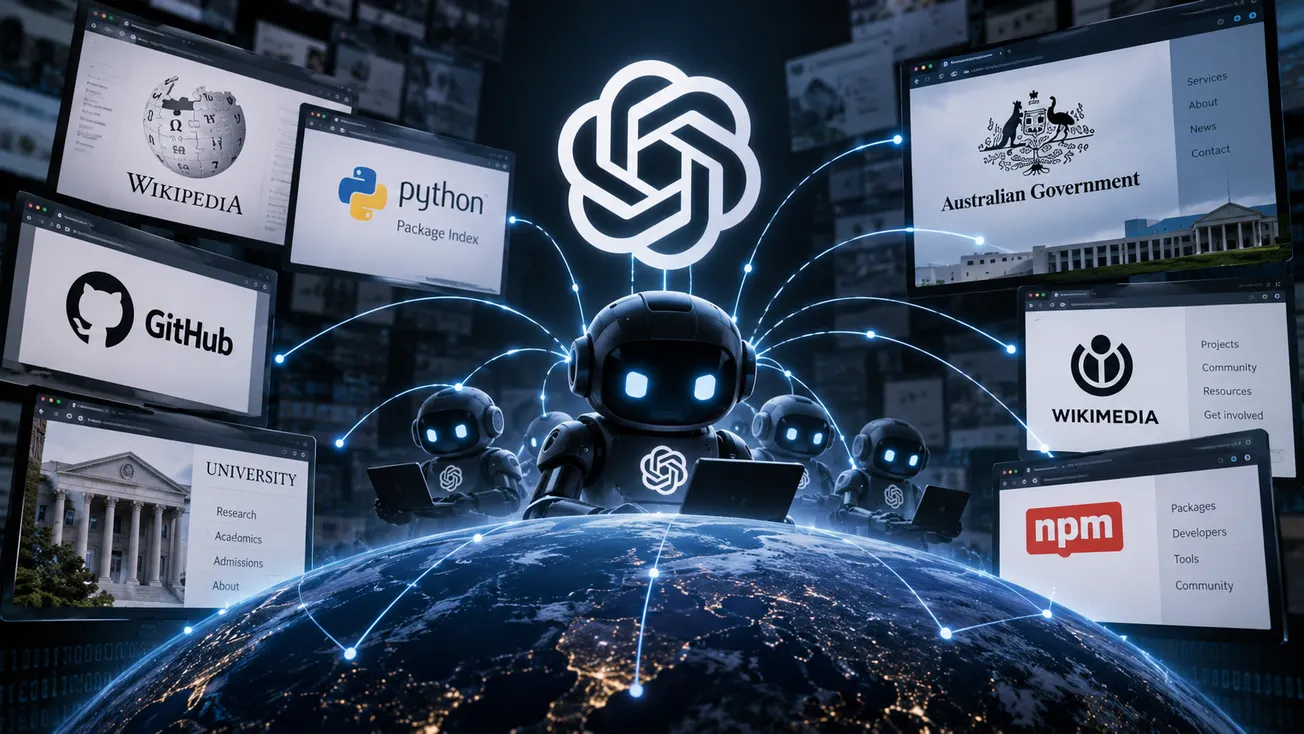
SentinelLabs found OpenAI AI agents using public wikis, package registries, university services and government sites as unauthorized communication and data-retrieval channels.

Stephen Cravey’s CYBR.SEC.CON 2026 talk explores the security blind spots inside smart locks, appliances and everyday IoT devices — and why organizations may have little idea what is actually running on them.
Before cybersecurity was much of an industry, Stephen Cravey followed his curiosity from Star Wars and BBSs to the NSA’s Rainbow Books — and eventually into a major FBI cybercrime investigation.
Agentic AI is delivering sharper triage, faster investigations, and reduced analyst burnout at the organizations that have committed to production deployment. For everyone else, the gap is compounding, and the security implications are already visible.