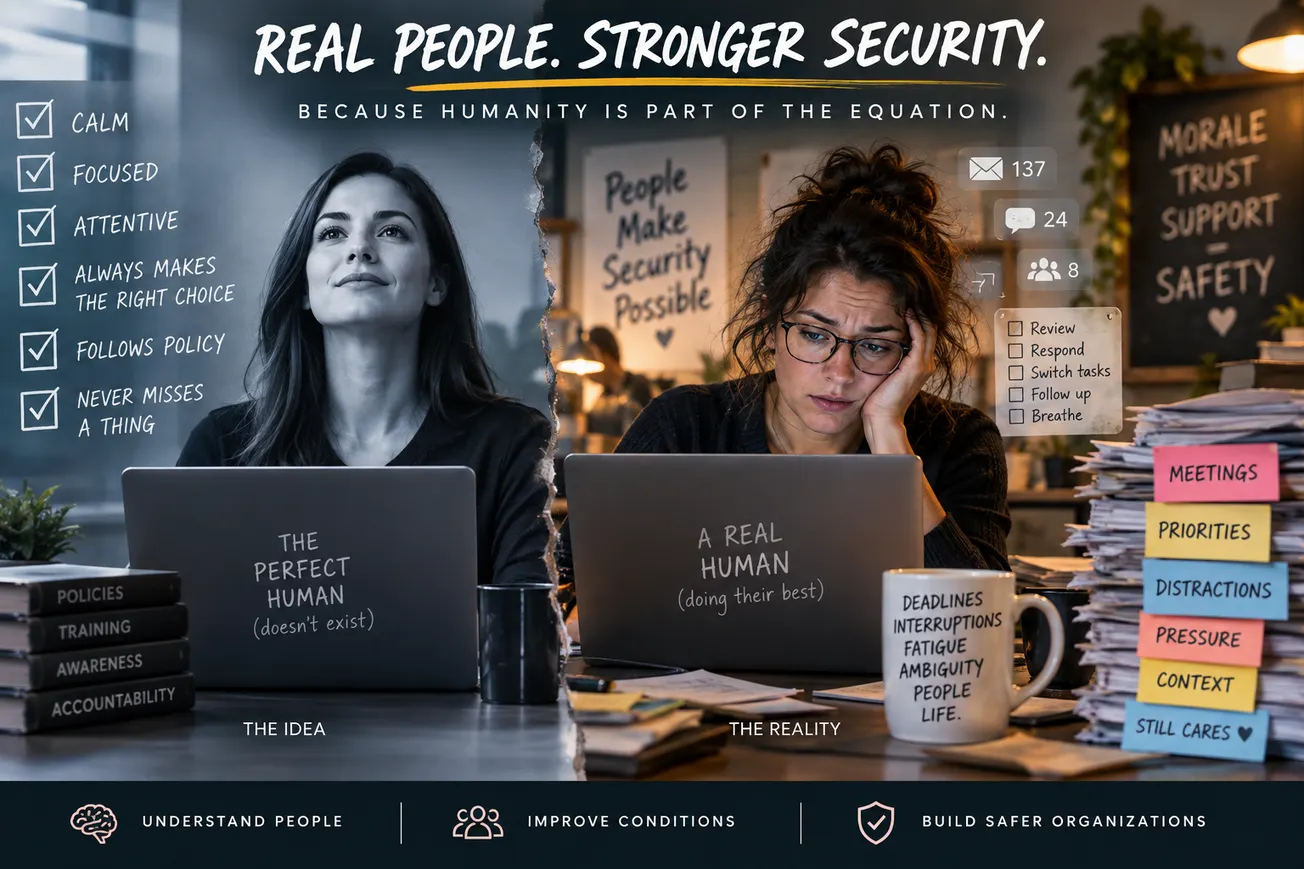
Cybersecurity organizations spend enormous amounts of time and money building controls, enforcing policies and training employees to make secure decisions. Yet those efforts often depend on an unrealistic assumption: that people will remain calm, focused and capable of making the right decision every time.
In the latest episode of CYBR.Minded, host Dr. Dustin Sachs and Shoshana Gourdin, owner and coach at Gourdin Coaching and a former technology operations leader, explored what happens when security programs are designed for an idealized human rather than the people actually doing the work.
Their central message: Morale, trust and workplace conditions are not peripheral management concerns. They directly influence whether security work gets done.
Full episode:
 , and CYBR.SEC.Media
The problem with the perfect human
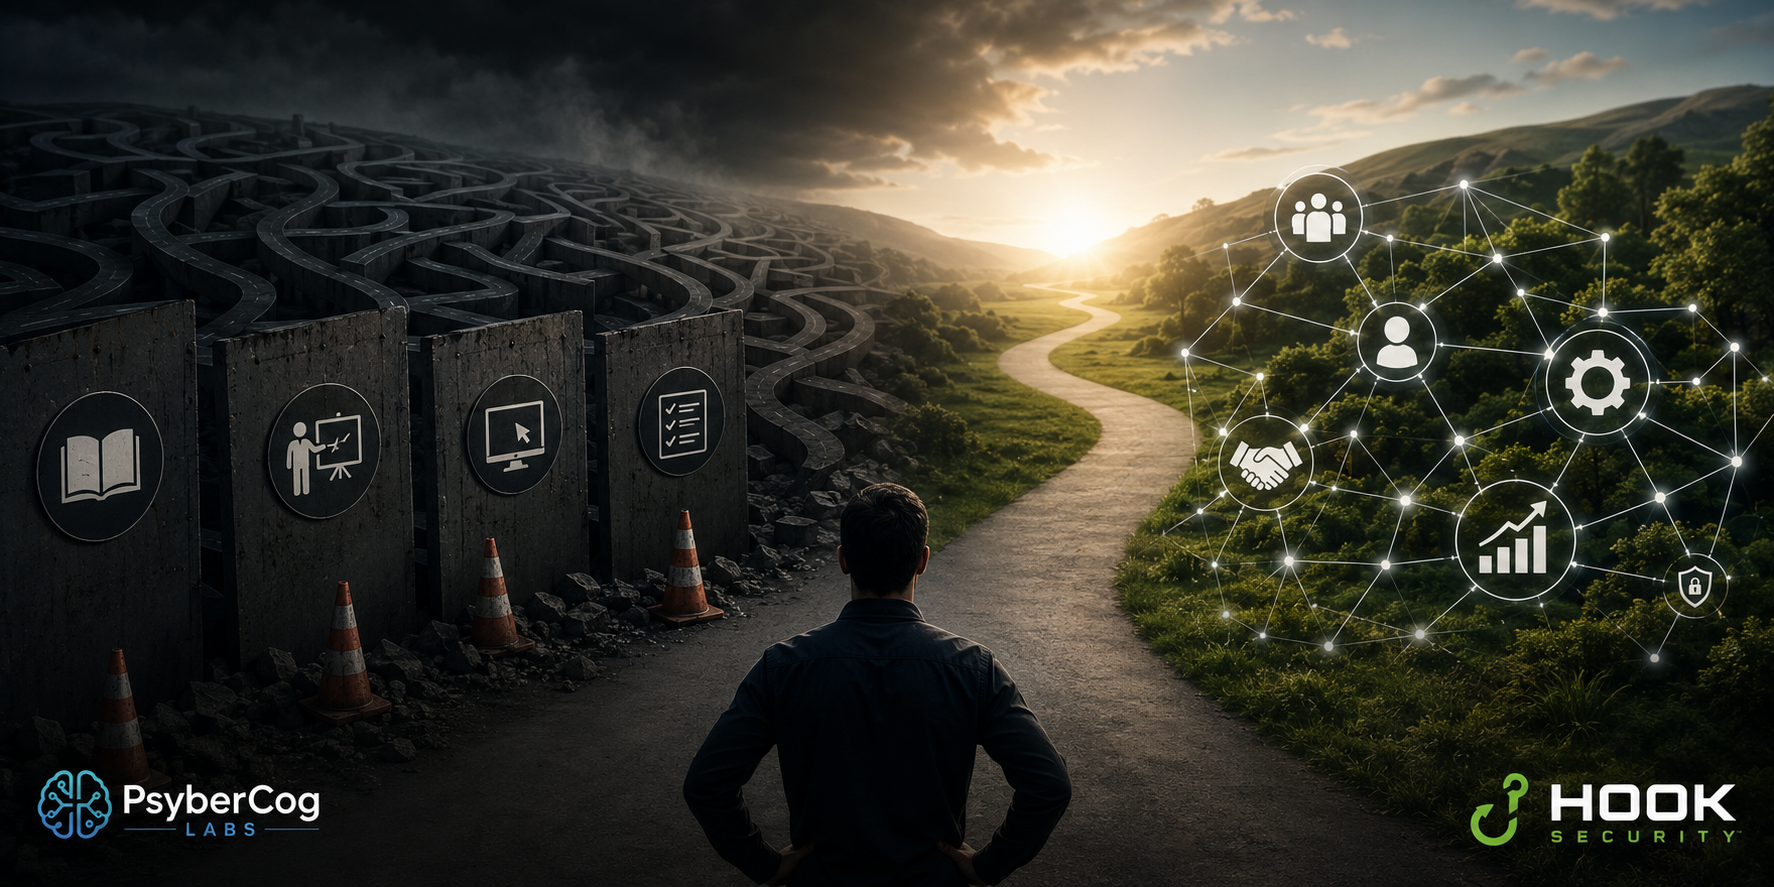
Security policies frequently assume employees can prioritize tasks, remember instructions, manage interruptions and follow through under pressure.
But real people experience fatigue, competing priorities, emotional stress and uncertainty.
Gourdin argues that security professionals themselves can overlook these realities because they often gravitate toward technical problems rather than interpersonal ones.
That becomes particularly problematic when organizations interpret mistakes as carelessness instead of examining the conditions that contributed to them.
Sachs frames the issue around executive function: the mental processes involved in starting and stopping tasks, planning, making decisions and following through.
Gourdin explains that everyone experiences occasional difficulties with these processes. Being highly capable in one area does not guarantee consistent performance across every task or situation.
The implication for security leaders is significant. Telling someone to follow a process does little good if the surrounding work environment makes following that process unnecessarily difficult.
Reward the behavior you want to see
One practical takeaway is the importance of recognizing employees who identify and report potential security problems.
Gourdin argues that organizations should spend more time rewarding positive behavior rather than focusing exclusively on mistakes.
"If you want your security professionals to pay attention when someone brings a strange problem to them, you have to reward them for it," she says.
Sachs recalls a phishing-awareness initiative at a Houston electric provider that recognized employees whose reports prevented potentially malicious emails from reaching thousands of colleagues.
The lesson extends beyond phishing. Employees need to know that raising concerns, questioning existing practices and reporting suspicious activity will be welcomed rather than punished.
That requires leaders to build trust before problems emerge.
Related:
 Dustin Sachs
 Michael Farnum
Measure outcomes, not just activity
Organizations routinely measure training completion, ticket closures and policy acknowledgments. Those numbers reveal little about whether employees can make effective security decisions when circumstances become difficult.
Gourdin suggests examining where work actually gets stuck and whether security teams maintain meaningful relationships with other departments.
She recalls discovering a potential Log4j exposure that colleagues dismissed because they believed the problem had already been resolved.
The underlying issue was not the technology. Security work had not been integrated into the team's normal workflow, leaving the concern without clear ownership.
For leaders, the takeaway is to examine how work gets done rather than simply assigning blame when something fails.
Start by asking why
Gourdin closes with a challenge for cybersecurity teams: examine who they are, what they are trying to protect and why their work matters.
Understanding those motivations, alongside the conditions shaping employee behavior, can help organizations build security programs that function in the real world.
The goal is not to eliminate human imperfection. It is to build security systems that account for it.