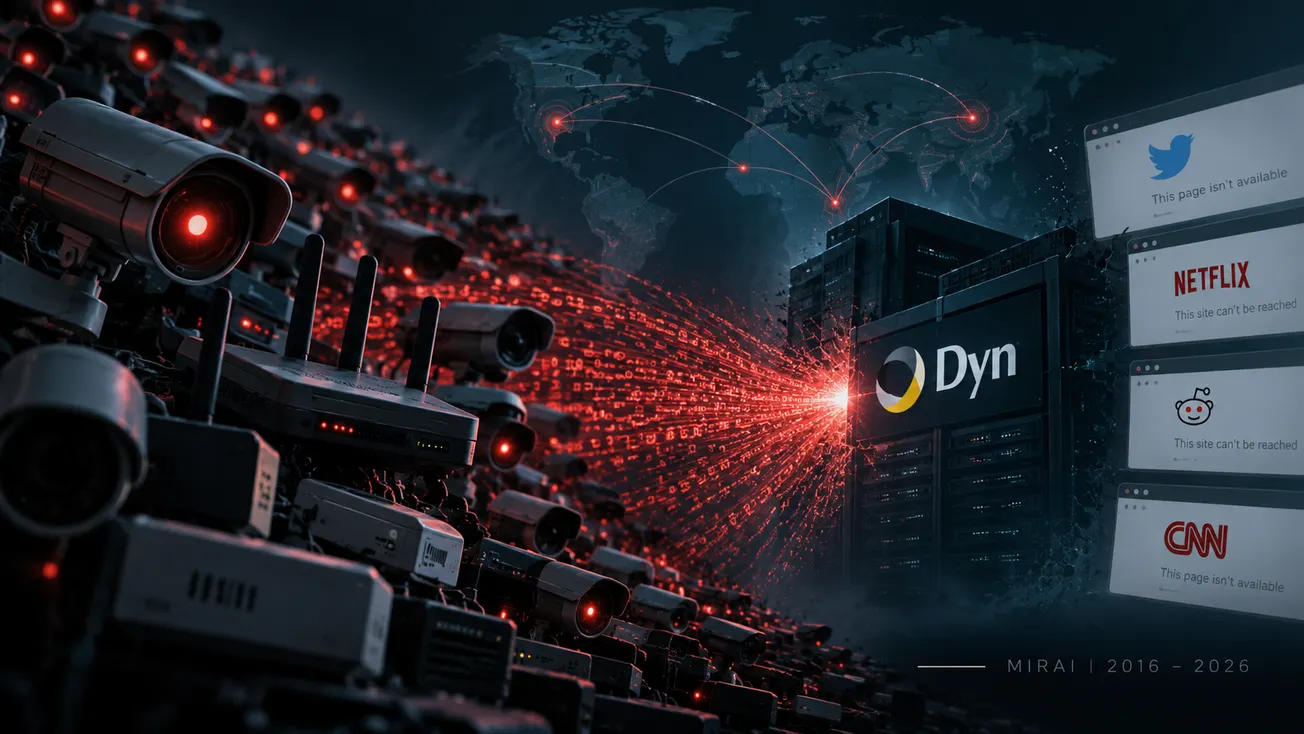
A Decade After Mirai: How the IoT Botnet Changed Cybersecurity Forever
Ten years after Mirai disrupted Dyn, explore how the IoT botnet changed DDoS defense, device security and internet resilience — and why it endures.
Ten years after Mirai disrupted Dyn, explore how the IoT botnet changed DDoS defense, device security and internet resilience — and why it endures.
DDoS attacks aren't just distractions. Learn why they reshape defender decisions and create opportunities beyond downtime.
This week: HOU.SEC.CON is now CYBR.SEC.CON, Cyber Sunday is now CYBR.Signal, and Chris Wysopal is done waiting for the industry to fix itself.
The biggest DDoS attacks grab headlines, but impact matters more than size. Learn what defenders should really measure.
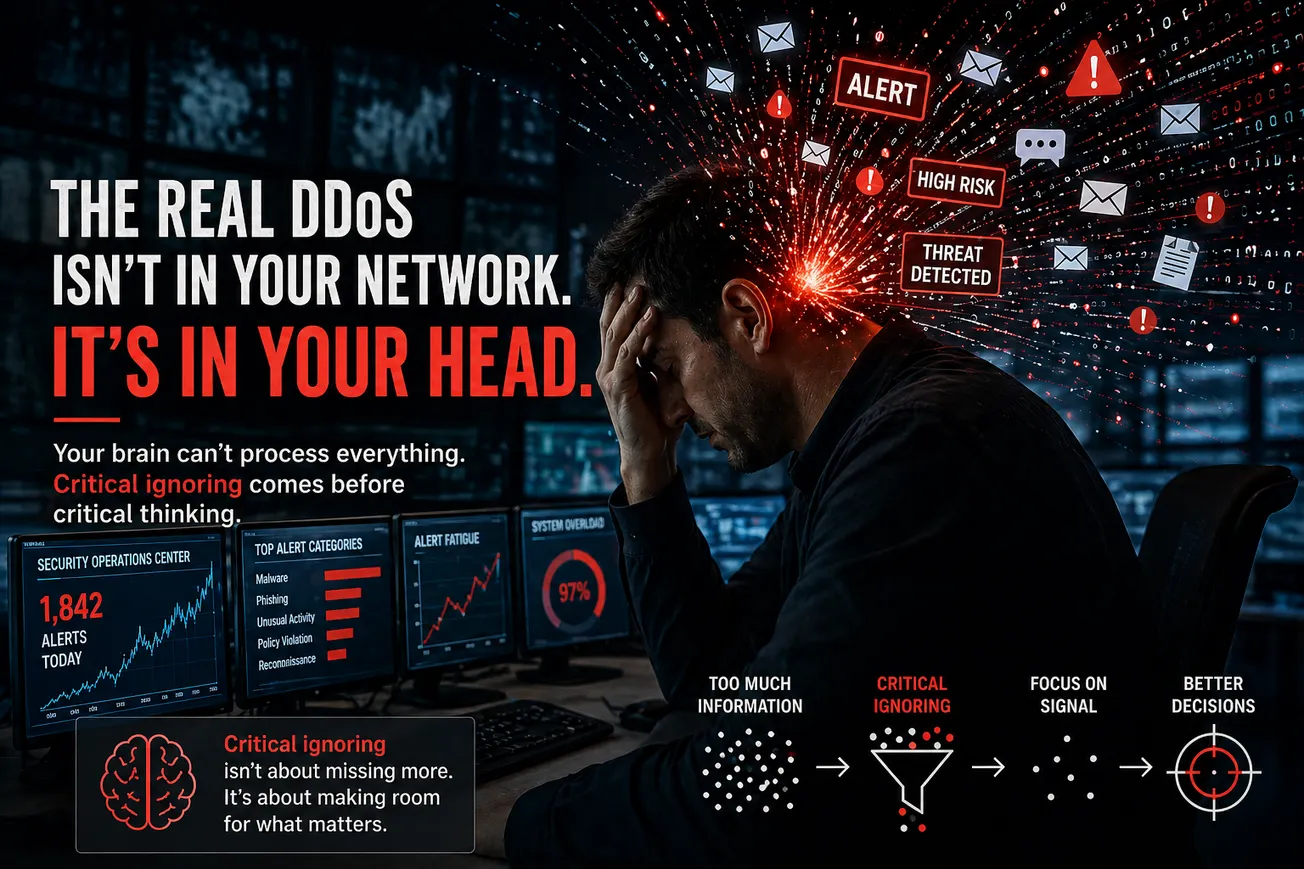
Security teams have spent years trying to reduce alert fatigue, but the real bottleneck isn’t tooling, but the human brain’s inability to process the volume of information being thrown at it.
Winn Schwartau argues that the biggest threat facing defenders isn’t just technical, but cognitive: overwhelming information flows that push humans into “mental DDoS.” He has introduced the concept of “critical ignoring” as a prerequisite to critical thinking.