AI Attacks Demand More Than Faster Patching, FireMon CEO Warns
As AI accelerates zero-day discovery and exploitation, FireMon CEO Jody Brazil says restricting network access is critical to defending vulnerable systems. (Sponsored by FireMon)
As AI accelerates zero-day discovery and exploitation, FireMon CEO Jody Brazil says restricting network access is critical to defending vulnerable systems. (Sponsored by FireMon)

Veracode's 2026 GenAI Code Security Report finds AI coding security improving for the first time, but persistent injection flaws and weak Java performance demand stronger security testing. (Includes infographic)

Endor Labs researcher Peyton Kennedy uncovered 14 vulnerabilities across seven AI platforms, exposing paths from prompt injection to remote code execution and data theft. (Sponsored by Endor Labs)

The eMudhra vulnerability exposed a years-long window of significant certificate risk. The PHP2Shell vulnerability is ubiquitous. Last week’s five vulnerabilities targeted many of the security controls assumed to be trustworthy.
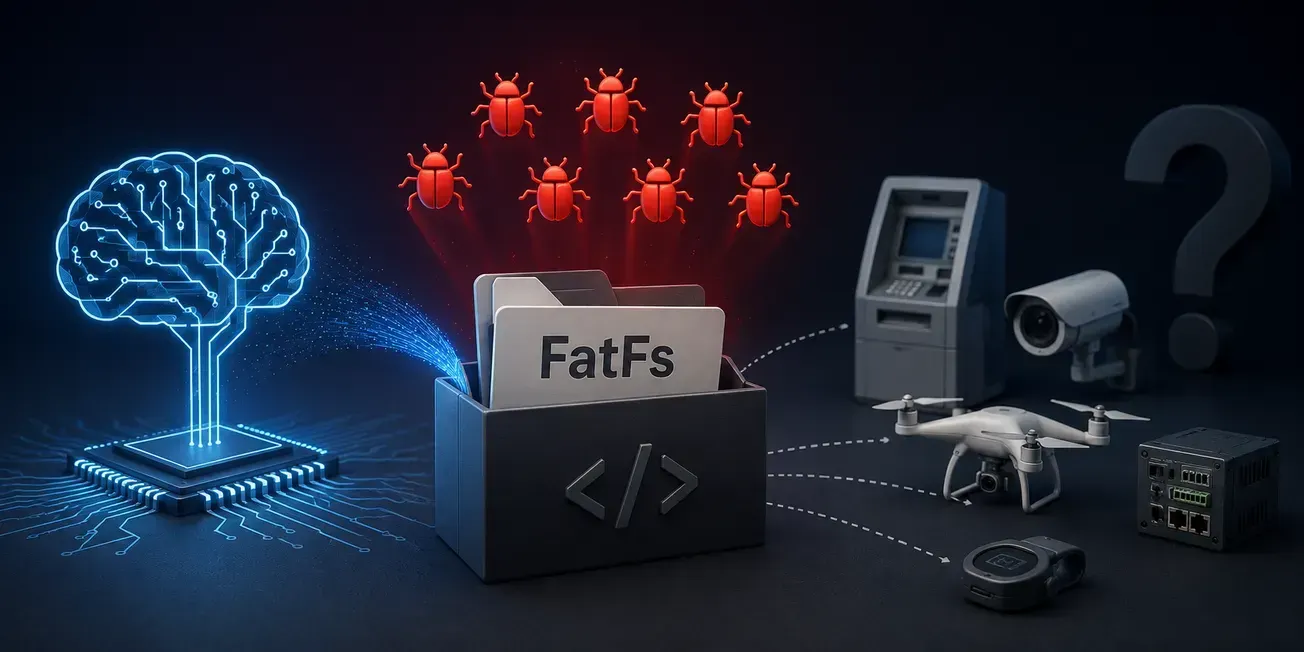
LLM-assisted bug hunting is uncovering critical vulnerabilities in old software such as FATFS, exposing a growing cybersecurity problem: AI is accelerating vulnerability discovery while patching and remediation struggle to keep pace.
Root Evidence analyzed 253,912 CVEs and found AI is accelerating vulnerability discovery, but not exploitation — exposing a vulnerability management model increasingly overwhelmed by noise.
Applications average 22 critical vulnerabilities while teams fix just 3.4 per month, exposing a widening AppSec gap that AI is making harder to close.
AI has broken traditional vulnerability management by accelerating vulnerability discovery and exploitation, but it may also be the only technology fast enough to help defenders regain the advantage.
New 1Password research found AI-generated vulnerability patches failed to fully fix complex software flaws 53.9% of the time, reinforcing the need for expert human review.