
Four days before PHP's security team planned to speak publicly, the attacks had already begun. Proof-of-concept exploits circulated twelve hours before the scheduled release, and attack traffic across Cloudflare's network climbed from thousands of attempts before public disclosure to hundreds of thousands in the hours after the public announcement. The patch window, the interval between when a fix ships and when exploitation begins, was barely existent.
The Internet was not yet done with defenders already weary from finding, assessing, and mitigating the PHP instances within their environments. Last week, PHP2Shell was one of five significant vulnerabilities disclosed or actively exploited. The CVSS 10.0 GitLab RCE (Remote Code Execution) vulnerability, tracing back to 2014; a memory-safety flaw in Node.js's bundled Brotli library; a use-after-free in Unbound's DNS-over-QUIC path; and the vulnerable state of eight eMudhra intermediate CA private keys arrived in rapid succession.
Each vulnerability is serious on its own; together, when they hit concurrently, remediation pipelines can't keep pace.
"The traditional vulnerability management process is going to have a hard time keeping up if it still involves someone reading an advisory, assigning a severity, opening a ticket, and waiting for the next maintenance window to apply a patch. That process was already struggling before the 'vulnpocolypse,'" Chris Wysopal, founder and chief security evangelist at Veracode, said. The disclosures within a few days meant many teams were still inventorying PHP2Shell when the GitLab, Node.js, Unbound, and eMudhra disclosures hit.
"The rate of technological change has exceeded the capacity of many organizations to understand, govern, and secure the environments they operate," said Michael Echols, CEO at Max Cybersecurity. That gap shows up as backlogged patches, untracked dependencies, and incident-response playbooks that still assume weeks of warning between disclosure and exploitation.
The PHP exposure is severe. Both CVEs sit in the core interpreter, putting them below the typical reach of application-layer defenses. In mod_php configurations, CVE-2026-109618 can execute before application code runs. Black Kite found roughly 1.37 million internet-facing PHP hosts that disclose a version; about 72.5% of those run end-of-life branches that no longer receive regular fixes.
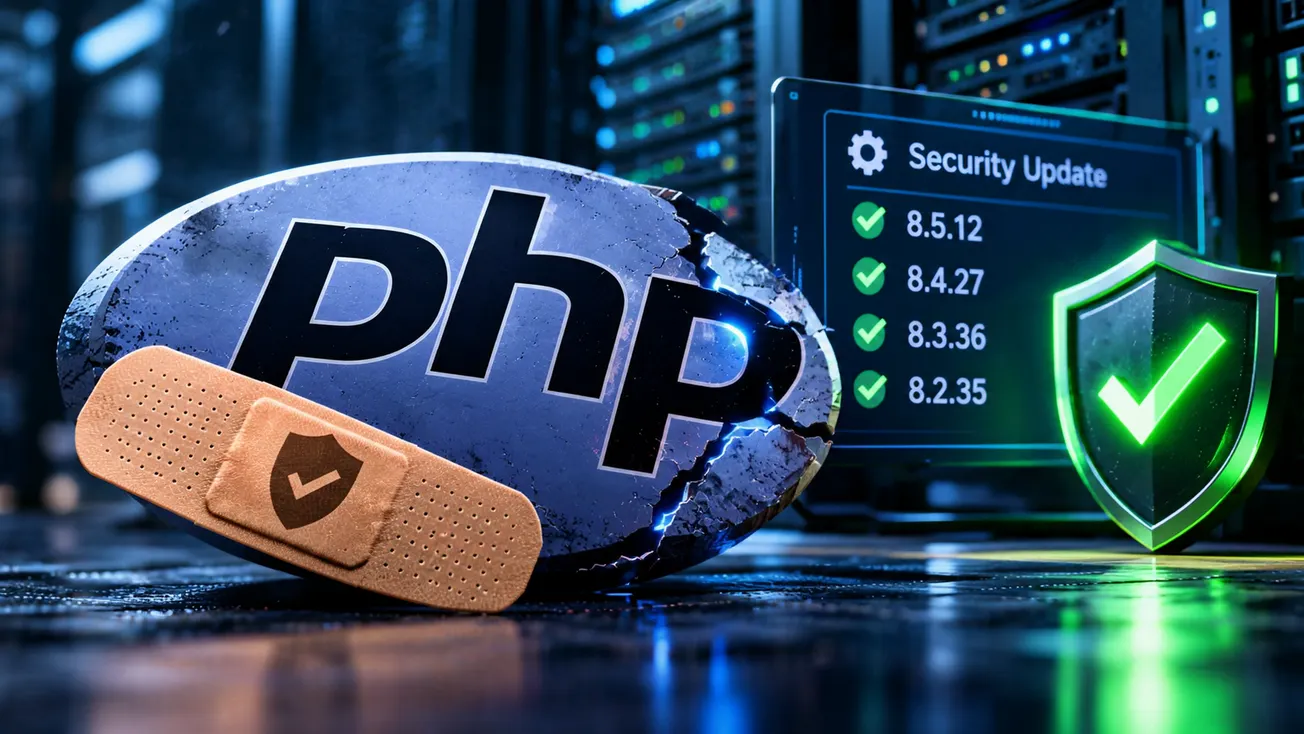
"PHP shows why fixing the problem can take considerably longer than identifying it," Rafay Baloch, CEO at RedSecLabs, said. "Updating WordPress or its plugins won't update the PHP runtime underneath. Until the fixes are installed, restrict access to vulnerable services and treat WAF rules as a temporary measure." Because exploitation traces back to Oct. 17, investigations should start from that date rather than from Oct. 21. CISA recommends updating immediately to PHP 8.5.12, 8.4.27, 8.3.36, or 8.2.35, or taking PHP-based systems offline.
The eMudhra exposure resulted from basic security protocol failures. Security researcher Ian Carroll found that eight eMudhra intermediate CA certificates had weak private keys that had been part of the Chrome and Mozilla trust stores. Some point to as far back as 2024, creating an extended window during which an attacker who recovered the keys could have issued trusted certificates. Browser makers responded rapidly: Chrome deployed a revocation update within two hours of notification, and Mozilla removed the affected root from NSS within days.
Beyond the Race to Patch
The harder part of remediation is the broader ecosystem: API clients, containers, build pipelines, and embedded devices that consume trust stores independently, update sporadically, and have no automatic browser revocation. "A compromised certificate authority can undermine trust in systems that are otherwise completely patched," said Wysopal. "We need to think carefully about where we've concentrated privilege and trust, and what happens when those assumptions fail."
Theresa Lanowitz, principal analyst, cybersecurity at Omdia, sees the same types of trust challenges defenders must face. "Trust is one of the key words going forward. Do organizations trust a patch? Do organizations trust the pathways of remediation to not impact something else? Do organizations trust agentic AI for autonomous remediation? Trust is the new frontier for AI and cybersecurity," she said.
CVE-2026-110264 is the fourth regex-related RCE the same researcher, joaxcar, discovered in GitLab in a single month. That cadence, security experts say, points to systematic, tool-assisted research rather than opportunistic discovery. "AI agents haven't brought much creativity to discovering vulnerabilities," said Jonathan Sword, director at Agility Cyber, "but they have shifted the time investment requirement substantially."
Enterprise defenders had no respite: the same week, Microsoft’s October Patch Tuesday addressed an estimated 1,415 CVEs, a new record according to ZDI, for a single month. By the same count, the company has crossed 1,000 in a single month for the first time, and more than in any prior full year of Microsoft vulnerabilities. Analysts at the Zero Day Initiative attribute the volume partly to AI-assisted discovery. The traditional remediation model- triage by severity, work the critical queue, let medium and low age- was built on the assumption that complex memory-safety bugs take time to weaponize.
"We're rapidly reaching a point where large organizations simply cannot scale up the people to keep up with the vulnerabilities being published," said Sword. "The answer to keeping secure used to be knowing your assets and organization inside out and tracking your risk. Now it's more about how fast you can mobilize expertise to unforeseen risks, where the arms race is in the attacker's favor." That shift means asset inventories and risk registers are still necessary, but no longer sufficient; speed of mobilization and savvy triage are becoming more decisive.
"We must move beyond vulnerability management as a patching exercise and toward continuous management of operational exposure. The future of cybersecurity will be determined less by how quickly we identify vulnerabilities and more by how effectively we control their consequences," Echols said. "I do not believe traditional vulnerability triage can scale indefinitely through additional personnel, more scanning, or faster patching alone. Organizations need better contextual intelligence, automation where appropriate, clearly defined decision authority, and governance that evolves with the systems being deployed," he added.
The practical implication for most enterprises is moving from patch management toward engineering systems that are simpler to fix. "We are not going to solve the 'vulnpocolypse' by hiring enough people to triage every new vulnerability," Wysopal said. "We have to engineer systems that are easier to understand, harder to compromise broadly, and faster to fix."