cybersecurity
Cloud Security Alliance’s SSCF Framework Hopes to Set a SaaS Security Baseline
The SaaS Security Capability Framework, released by the CSA's SaaS Working Group provides an industry-standard set of baselines, customer-facing security controls for SaaS platforms.
How NIST's AI Control Overlays Interface with the Coalition for Secure AI
The National Institute of Standards and Technology's new Control Overlays for Securing AI Systems and the Coalition for Secure AI provide much-needed standardization for AI security across government and industry.

The Salesloft Drift Breach Expose Critical Flaws in OAuth Implementations
For enterprise security teams already struggling with SaaS sprawl and third-party risk management, the Drift breach is a reminder that OAuth tokens—designed to enhance security by eliminating password sharing—are high-value targets.
Successfully Managing Machine Identities in an AI-Driven World
Unlike human identities, which grow linearly as the workforce expands, machine identities proliferate exponentially as organizations embrace automation, microservices architectures, and AI-powered tools. This raises new identity governance challenges.


The Tier Trap: How the Most Popular Cybersecurity Framework Gets Misused
Treating CSF Tiers as maturity scores creates a dangerous illusion… boards believe Tier 4 means secure, when in reality it does not.
Analysis: How to Bulletproof a Security Program Against Vendor Consolidation
Most, eventually all, CISOs will be forced to endure the loss of a cherished vendor and promising roadmap due to an acquisition.
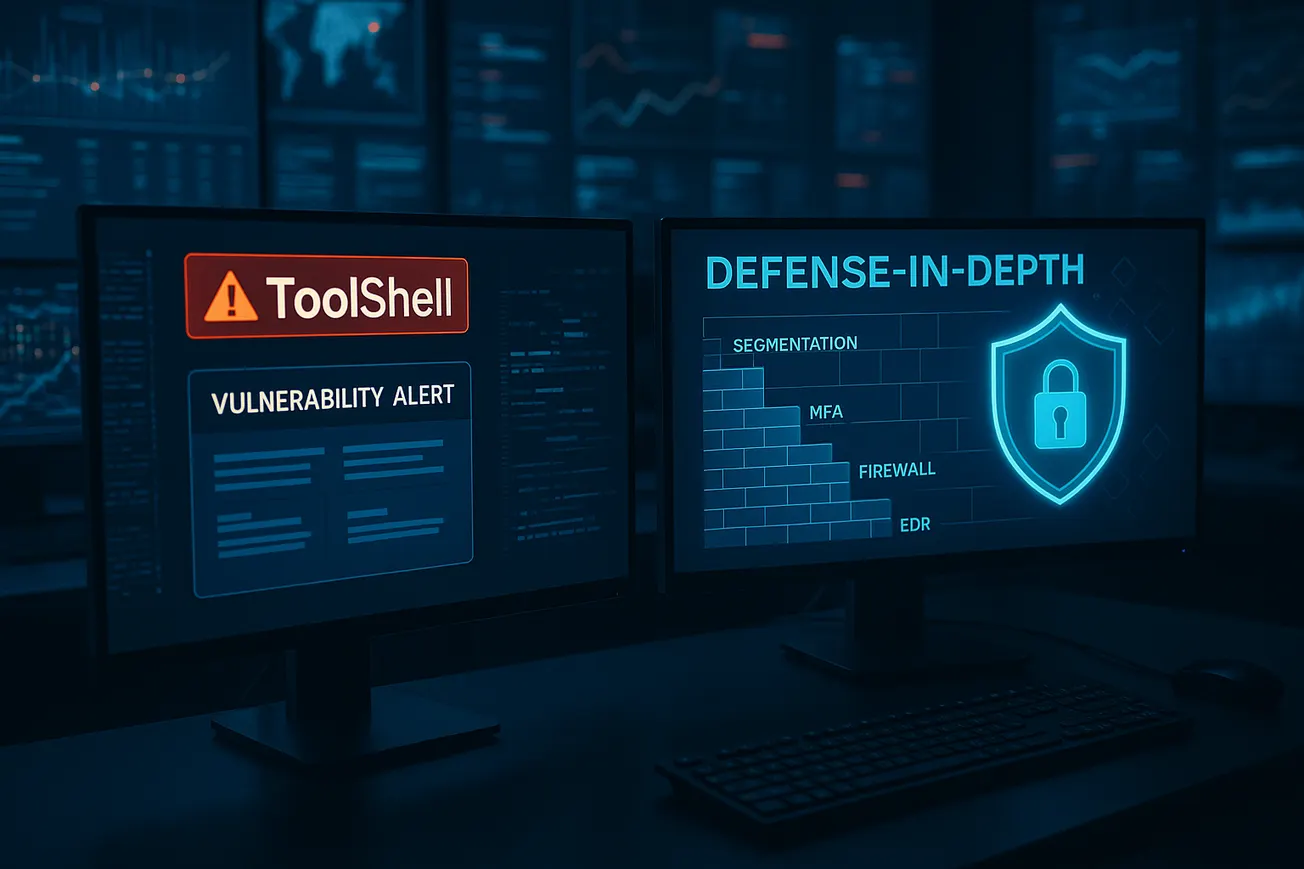
Bolster Defense-in-Depth Strategies as Collaboration Platforms Face Escalating Threats
It’s their necessity for such accessibility that makes secure configuration especially challenging—and when a zero-day vulnerability emerges, the damage can be swift.
Structuring a Unified Cybersecurity Program Across IT and OT Environments
Cybersecurity programs are most effective when they serve more than a compliance function. In public utilities and other critical infrastructure environments, the program must support operational reliability, safety, and public trust.