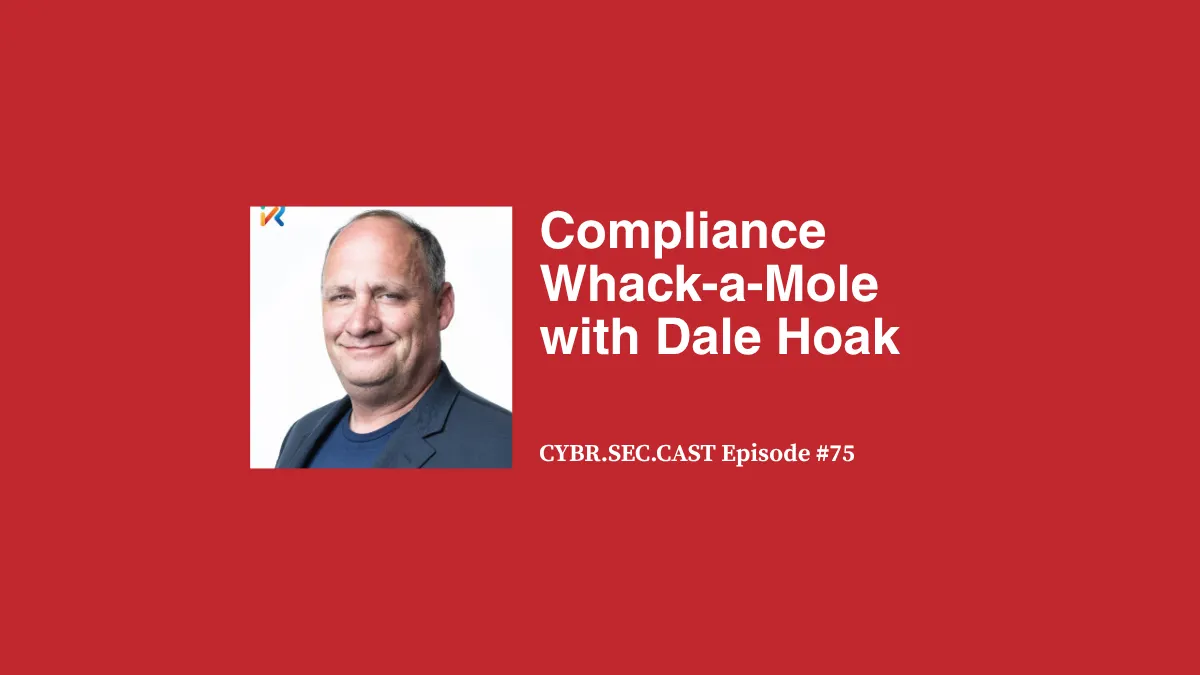
In this episode of CYBR.SEC.CAST, Michael Farnum and Sam Van Ryder sit down with Dale Hoak, CISO at RegScale, to explore why compliance should be the starting point for cybersecurity - not the finish line. Dale discusses the shift from checkbox auditing to continuous cyber resilience, the growing impact of AI on risk, and why security, compliance, and business leaders need to work from the same playbook. The conversation also dives into executive buy-in, board-level risk discussions, and the importance of becoming an agent of change inside your organization.
Related articles:
 Bill Brenner
 Bill Brenner
Things Mentioned:
- RegScale - https://regscale.com
Do you have a question for the hosts? Reach out to us at media@cscgroupllc.com
In this episode:
- Host: Michael Farnum
- Host: Sam Van Ryder
- Guest: Dale Hoak
- Director: Bill Brenner
- Producer: Lauren Andrus
- Music by: August Honey
Keep up with our Conferences and Events:
Keep up with CYBR.SEC.Media:
Learn About CYBR.SEC.Careers Non-Profit Efforts
Subscribe to the podcast:
Listen to our other shows:
Thank you to our Media Partners:
CYBR.SEC.CON.
CYBR.SEC.CON. and OT.SEC.CON.
CYBR.SEC.CON. and CYBR.HAK.CON.