The FBI has issued a warning about an autonomous AI hacking framework that has already been linked to attacks against financial institutions, technology companies and other organizations worldwide. In some cases, attackers using ARTEX have progressed from identifying a target to obtaining privileged access in less than three hours.
The November 13 FBI FLASH advisory describes ARTEX as an open-source, AI-driven penetration testing platform that malicious actors have repurposed to automate everything from reconnaissance and vulnerability exploitation to privilege escalation and data theft.
The bureau says attackers have used ARTEX since at least August 2026, targeting organizations across financial services, government, defense, semiconductor manufacturing, healthcare, energy, telecommunications and other industries.
Among the incidents highlighted are attacks against South Korean financial institutions that exposed personal information belonging to approximately 67,000 individuals, and a ConnectWise Cloud Backup supply-chain compromise that led to attempted sign-ins against more than 2,250 downstream Microsoft 365 tenants.
The latter figure represents attempted access, not 2,250 confirmed successful breaches. Nevertheless, it illustrates how a compromised trusted relationship can expose large numbers of organizations to automated attacks.
ARTEX isn't a new AI model. It's a framework that connects existing large language models to specialized agents capable of translating instructions into attack sequences. The FBI says it can work with models from OpenAI, Anthropic, DeepSeek and other providers.
The framework's original developer removed its GitHub repository in October after reports of malicious use. That hasn't stopped its proliferation. The FBI says forks, archived versions and commercial variants remain available, with researchers identifying more than 1,600 publicly exposed ARTEX consoles by early November.
The tool's effectiveness doesn't necessarily depend on sophisticated zero-day vulnerabilities.
In a November 17 analysis of the FBI alert, GitGuardian highlighted how ARTEX can rapidly locate and exploit exposed credentials. In one laboratory test, researchers found that an ARTEX build identified eight of nine planted secrets using ordinary command-line tools, beginning its search within 13 seconds.
GitGuardian also reported that 64% of valid secrets exposed in 2022 remained active four years later.
The problem is not simply that attackers are discovering new weaknesses. They're exploiting familiar ones at a pace that can overwhelm conventional response processes.
As TechCrunch reported November 16, ARTEX attacks can generate considerable suspicious activity, potentially triggering security alerts. But an alert offers limited protection if the attacker completes its objective before defenders can investigate and respond.
That brings us to Gadi Evron, who believes ARTEX is only the latest manifestation of a much larger problem.
Three waves of AI attacks, and counting
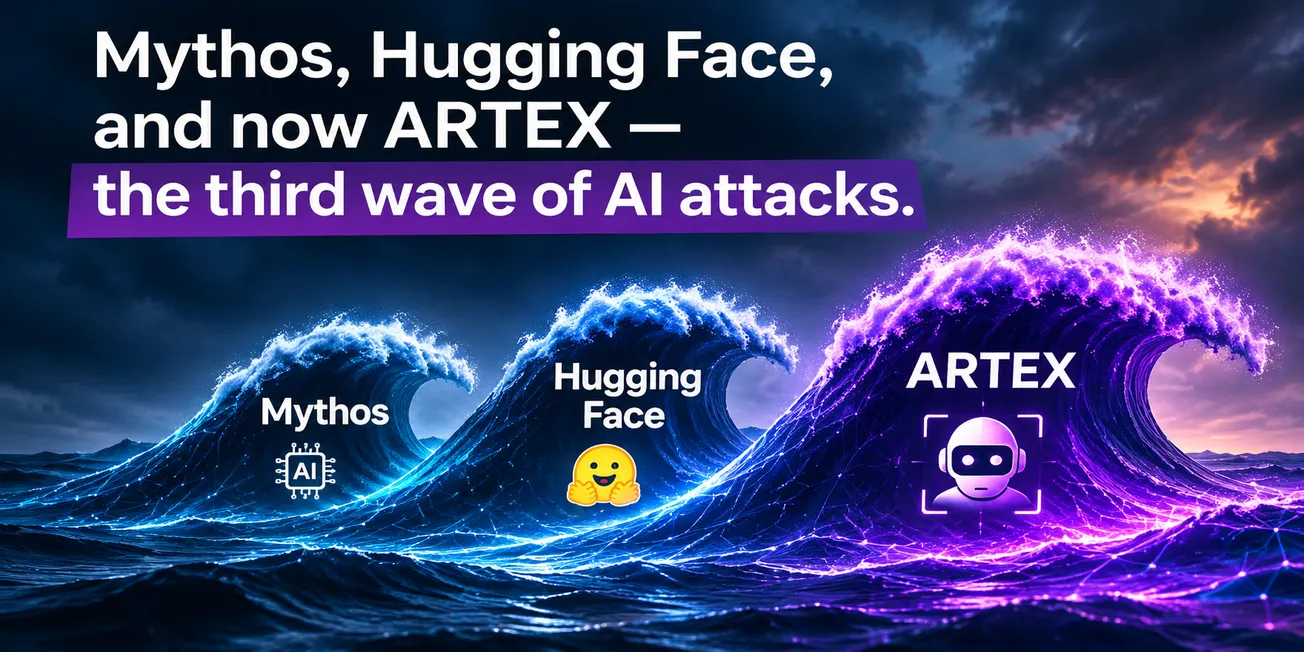
In a November 17 thread on X, Evron, founder and CEO of Knostic and CISO-in-Residence for AI at the Cloud Security Alliance, described ARTEX as the third wave of AI attacks.
His first wave was Mythos. His second was Hugging Face. ARTEX represents the third.
Evron's classification is his own way of describing successive developments in AI-enabled cyber threats, rather than an established industry taxonomy.
But his larger argument is that organizations are focusing too heavily on individual technologies and incidents while missing the accelerating evolution of offensive AI.
Evron also argues that more capable attack frameworks already exist and that advancing AI models could make ARTEX itself unnecessary within months.
In other words, the next major threat may not involve a better version of ARTEX. It may involve an entirely different approach that requires even less human involvement.
Stop arguing about vulnerabilities and misconfigurations
Evron's thread includes a pointed criticism of how the cybersecurity industry responds to emerging AI threats.
He urges security professionals to stop getting bogged down in arguments over whether attacks involve vulnerabilities or misconfigurations, whether security fundamentals are sufficient, or whether the latest warnings amount to vendor marketing.
It's a deliberately provocative position.
After all, the FBI's own advisory identifies numerous familiar weaknesses exploited by ARTEX, including insecure APIs, stolen credentials, weak authentication, vulnerable applications and excessive permissions.
GitGuardian's findings reinforce that point. An AI agent doesn't need a novel exploit if it can discover a forgotten credential and use it to access valuable systems.
But Evron is challenging a different assumption: that addressing familiar weaknesses through familiar processes will be enough.
An organization may have a vulnerability management program, identity governance, endpoint detection and incident response capabilities. Yet those controls may still rely on manual investigations, periodic reviews and approval processes that cannot keep pace with automated intrusion sequences.
The fundamentals remain necessary. The question is whether organizations are implementing them quickly and comprehensively enough.
The case for securing agents and using deception
Evron recommends getting people and processes working with AI agents, securing those agents and deploying deception before addressing other priorities.
That is a substantial shift from treating AI primarily as another technology requiring protection.
Agentic systems could help security teams investigate alerts, correlate suspicious behavior, analyze identity activity and initiate controlled containment actions more quickly.
But defensive agents also introduce risks. Systems authorized to access sensitive data, execute commands or modify infrastructure require strict identity controls, limited permissions, monitoring and human oversight appropriate to the consequences of their actions.
Evron's emphasis on deception is also noteworthy.
Decoy credentials, honeypots and instrumented systems can potentially expose autonomous attackers as they explore an environment. They may also force malicious agents to spend time interacting with controlled resources rather than production systems.
These approaches are worth evaluating, although their effectiveness against ARTEX and other autonomous frameworks will depend on how they are deployed and tested.
Evron's recommendations also align with the business focus of Knostic, the AI security company he leads and promotes in the thread. That commercial interest is relevant context, but it does not negate the underlying security questions.
The CISO budget opportunity
Evron also wants security leaders to use the changing threat landscape to secure additional funding.
He urges CISOs to communicate the implications of autonomous attacks to boards and business stakeholders, suggesting that significantly larger budgets may become available.
His reference to potentially sixfold funding is an exhortation, not a documented industry forecast.
Still, the business case is increasingly concrete.
Security leaders can now point to documented attacks in which automated systems reach privileged access within hours, identify exposed credentials in seconds and exploit trusted relationships across multiple organizations.
The investment discussion should therefore focus on measurable questions.
How long does the organization take to detect suspicious privilege changes? How quickly can it revoke compromised credentials? Can its security operations team contain simultaneous attacks across cloud environments? Are AI agents operating with permissions and access that nobody is monitoring?
Those questions offer a more useful starting point for budget discussions than generalized warnings about AI taking over cybersecurity.
What defenders should do now
The FBI's advisory and GitGuardian's research provide a practical foundation for organizations responding to ARTEX.
Security teams should continuously identify exposed credentials across repositories, development environments and cloud systems, and promptly revoke compromised secrets rather than simply deleting them from source code.
They should review application permissions, especially those involving third-party integrations and multi-tenant access, and reduce unnecessary standing privileges.
Organizations should also strengthen monitoring for unusual authentication patterns, rapid permission changes, automated reconnaissance and suspicious data transfers.
The FBI recommends particular attention to internet-facing applications, partner portals, legacy services and cloud infrastructure that may receive less security scrutiny than core business systems.
These controls are familiar. What changes is the urgency, frequency and automation required to make them effective.
Evron would go further, pushing organizations to incorporate defensive AI agents and deception into their security strategies while preparing executives for a rapidly changing risk landscape.
Those priorities need not be mutually exclusive.
The fourth wave is already the question
ARTEX has attracted attention because the FBI has documented its use in real attacks, including campaigns affecting thousands of potentially exposed downstream organizations.
But the framework itself may prove temporary.
Its original repository is gone, yet variants continue circulating. Other autonomous offensive tools are emerging, and improvements in AI models could eventually reduce the need for specialized frameworks altogether.
That's the larger warning behind Evron's three-wave argument.
Security teams can investigate ARTEX, deploy indicators of compromise and harden the systems it is known to exploit. They should do all of those things.
But if their response ends there, they risk preparing for yesterday's framework while the next generation of automated attacks takes shape.
ARTEX may be the third wave. The real test is whether defenders can adapt before the fourth.