It’s a case study detailing why detecting an attack and then running the traditional endpoint playbook is no longer enough. After the Binance team discovered an anomaly on a DevOps engineer’s laptop, they took the traditional steps: they replaced the impacted endpoint and rotated the engineer’s credentials. It was case closed. Only it wasn’t.
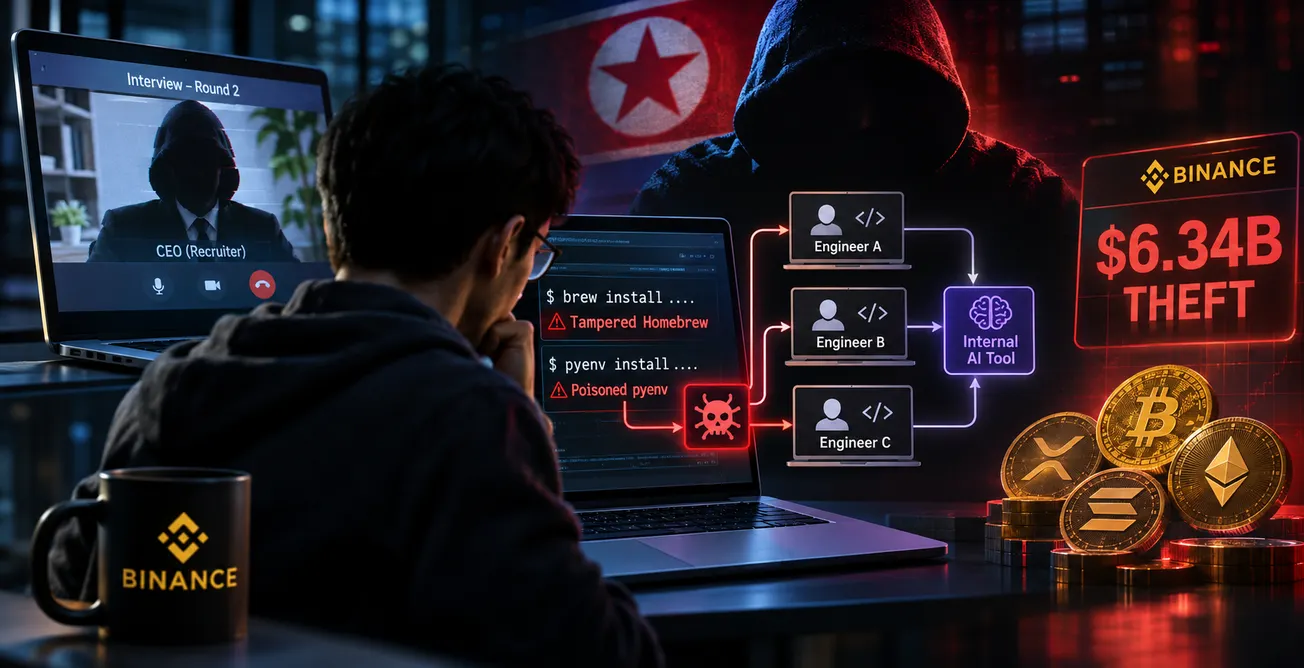
This week, Binance detailed how a DevOps engineer downloaded a tainted Homebrew installation, followed by a social engineering attack disguised as recruitment, which led to the $6.34 billion theft of cryptocurrency from the world’s largest cryptocurrency exchange.
“Automated money movement now outruns investigators, making fast, machine-readable indicator sharing more valuable than the attribution itself,” wrote Eric Parizo, president and chief analyst, at Cernivera Research in his daily note. “For North Korea, crypto theft is a sanctioned revenue stream, and large exchanges remain its prime target.”
In June, a Binance wallet DevOps engineer searched for an AI coding tool, clicked a search-engine ad, and installed a tampered copy of Homebrew, a popular package manager for Macs. Engineer A, a member of Binance’s Wallet DevOps team, downloaded the tampered Homebrew installer while setting up an AI coding assistant.
Binance says it caught the June intrusion quickly. It replaced the device and rotated credentials. However, the attackers learned that Engineer A worked on wallet infrastructure, and so did his colleagues.
In September, the attacker used a different opening. A second engineer, on a job-hunting platform where his profile mentioned Binance, was contacted by someone posing as a project director. In the first-round video interview, a supposed HR representative shared a social-media account full of personal photos to build trust. The second round, on a chat app, was with the self-described CEO of a company that didn't exist.
Engineer B was instructed to download an assignment to his work computer. The repository replaced a component of pyenv—a common tool developers use to manage Python versions—with a malicious copy that connected to an attacker-controlled server. Binance says the malware was previously unknown and evaded its endpoint-protection software, and that the attacker removed forensic traces.
Later, the attacker used Engineer B’s machine and an internal AI tool as what Binance calls a springboard, gaining control of Engineer A and a wallet software engineer, Engineer C. Engineer A’s computer held the container-deployment token.
“Work devices should be used for work only, never for personal tasks, and above all never for a job interview,” said Parizo. “More broadly, teams should learn to spot a multistage campaign for what it is; catching one intrusion, as Binance did in June, doesn't mean the attacker is gone.”
The theft began on Oct. 29, between 17:15 and 19:56 UTC; the attacker logged in to Engineer C’s machine, used the token to deploy a container, and triggered a malicious script. That gave access to Binance’s internal wallet-signing service, which can authorize transactions outside the normal withdrawal process.
How Binance’s defense and response broke down
Between 20:05 and 20:09 UTC, five hot wallets sent 233.46 million XRP to an attacker-controlled address. Solana and Optimism wallets followed. Although alerts were triggered, another hot wallet sent 18,270 BTC.
The attacker then exploited a newer Ethereum feature called EIP-7702, which lets an account delegate some execution rights to a smart contract. Through the signing service, the attacker submitted 50 signed authorizations that manipulated the account transaction counter (a nonce) and set malicious delegations. Because the authorizations lived on the blockchain, suspending withdrawals couldn’t revoke them. And Binance’s hot wallets use multi-party computation, or MPC, a method that splits key material among multiple parties, so no single person holds a full key; there was no single private key to turn off. Binance was forced to build and execute a specialized revocation procedure. The last unauthorized transfer, 2,961.9 ETH, completed at 23:56 UTC; the delegation was cleared at 00:10 UTC on Oct. 30.
Binance says about $2.85 billion has been frozen or intercepted and that 98% of affected token assets had been replenished by Oct. 31. It also relays the FBI’s finding that North Korea was responsible.
Binance’s initial June response followed the standard playbook: find the infection, replace the device, rotate credentials. But the attacker retained a map of the organization. Four months later, Engineer A was targeted again, and the token on his computer opened the signing service.
Inadequate defenses of developer workstations. Engineer A’s machine held a token that could deploy into wallet infrastructure. Engineer B ran interview code on a work laptop after being found through a profile that named his employer. For attackers, a developer’s machine is a production-adjacent asset.
The third is that internal AI tools are part of the attack surface. Binance says the tool enabled an attacker on one engineer’s computer to gain control of two others. While the report doesn’t explain how, the implication is clear: an assistant with that reach functions as essentially a network bridge.
The broader lesson applies beyond crypto. Long-lived grants and delegated permissions are everywhere in enterprise computing: OAuth consents, API tokens, federated trusts. When an attacker controls the system that issued them, revoking them requires more than shutting a system down.
Binance says its security team blocked 57 suspected North Korea-linked cases in 2026 using fake interviews, malware disguised as developer tools, tampered packages and browser extensions, and fake video software. Each targets an employee’s machine, and developers’ machines sit closest to production.
“The entry points were ordinary – a poisoned open source installer and a fake recruiter – so what matters is endpoint anomaly detection that flags files straying from known-good versions, and basic employee hygiene,” Parizo said. “Any firm that handles digital currency also has to be technically ready to halt a wallet-draining theft fast. For Binance, shaving even an hour off the four-hour drain might have saved it billions,” he concluded.