This article is based on a conversation between Dr. Dustin Sachs and Joshua Copeland on CYBR.Minded, part of the CYBR.SEC.Media podcast lineup. Full episode:
 , and CYBR.SEC.Media
Cybersecurity teams are expected to follow procedures, meet compliance requirements and respond to threats with precision. But what happens when that discipline becomes an expectation that everyone must think and work the same way?
Organizations risk missing the very signals they need to detect threats.
That's the central argument emerging from the latest episode of CYBR.Minded, where host Dr. Dustin Sachs speaks with Joshua Copeland, cybersecurity director, educator and retired U.S. Air Force cyber professional, about why effective security teams need both operational discipline and independent thinking.
Their discussion challenges a familiar assumption: that consistency in cybersecurity requires uniformity among the people doing the work.
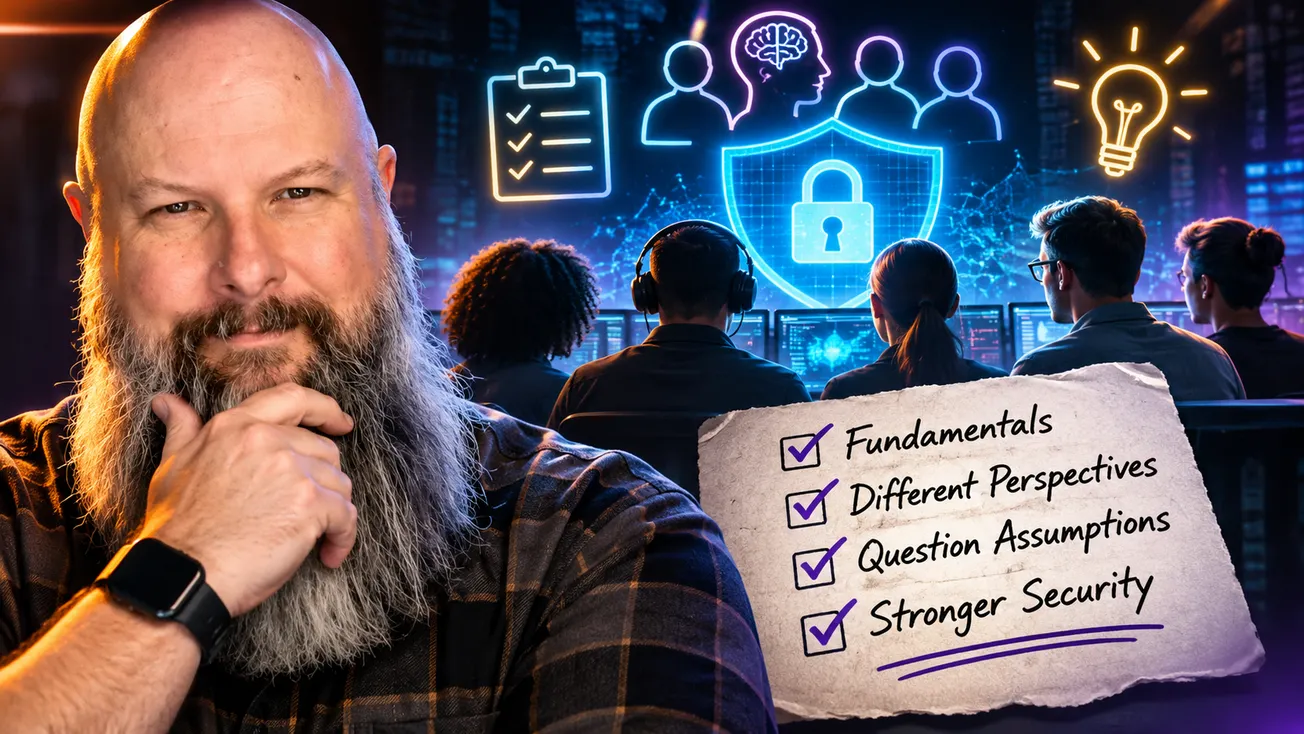
Instead, Copeland argues that organizations should get the fundamentals right while giving employees room to approach problems from different angles.
Cybersecurity discipline starts with the basics
Copeland's military experience provides a useful starting point.
Military organizations depend on standardized procedures, clear communications and the ability to execute under pressure. Those practices have obvious applications in cybersecurity, particularly during incident response and other high-stakes operations.
But Copeland sees a fundamental problem in how civilian organizations apply that discipline.
They frequently pursue new technologies and security trends without mastering the basic operational practices that make those investments effective.
Do they know what assets they have? How those assets are configured? Who owns them? Whether service accounts have appropriate permissions?
Copeland points to configuration management databases, endpoint inventories and access controls as examples of fundamentals that organizations should already have under control.
Yet security teams continue chasing the latest innovations showcased at conferences such as RSAC and Black Hat while struggling to answer those elementary questions.
The lesson isn't that cybersecurity needs more rigid procedures. It's that discipline must produce operational results.
A completed checklist means little if the organization still doesn't know what it's protecting.
Sachs takes that argument further, pointing out that organizations frequently create the appearance of discipline without establishing the conditions needed to make it effective.
Annual training completion, policy acknowledgments and compliance documentation can demonstrate that employees followed instructions. They don't necessarily demonstrate that employees understand the risks or will make good decisions under pressure.
When organizations care more about recording training completion than whether employees learn anything, they risk undermining trust in the security program itself.
Why different perspectives make cybersecurity teams stronger
For Copeland, the distinction between discipline and conformity becomes especially important when building cybersecurity teams.
Hiring people with similar backgrounds, credentials and professional experiences may create a team that communicates comfortably and approaches problems consistently.
It can also create blind spots.
Copeland describes cybersecurity problems as multidimensional. Different people approach those problems from different directions, potentially uncovering weaknesses that others overlook.
One analyst might identify an unusual pattern in system activity. Another might recognize an architectural weakness. A third might challenge an assumption everyone else has accepted.
Together, those perspectives can produce a more complete understanding of the threat.
The value isn't simply having people disagree. It's creating an environment where different approaches can be tested against one another.
When people independently examine a problem from different angles and arrive at the same conclusion, Copeland argues, that convergence provides greater confidence in the result.
Sachs connects that observation to research methods, particularly triangulation, in which multiple perspectives or sources of evidence strengthen the trustworthiness of findings.
The cybersecurity implication is straightforward: A team that thinks alike may reach agreement quickly, but agreement alone doesn't establish that its conclusions are correct.
Neurodiversity can reveal security signals others miss
That discussion leads to one of the episode's most consequential themes: neurodiversity as an operational advantage.
Both Sachs and Copeland speak openly about their own neurodivergence and the importance of recognizing different cognitive strengths.
Copeland describes the analyst who notices something unusual in a security operations center and refuses to let it go.
Automated systems might not recognize the activity as malicious. Other analysts might dismiss it as noise.
But someone with an aptitude for spotting anomalies and pursuing unexplained patterns may identify the early signs of a breach.
The same principle applies elsewhere in cybersecurity.
Someone who naturally looks for exceptions and loopholes may be particularly effective in governance, risk and compliance. Someone who approaches systems unconventionally may identify weaknesses overlooked by colleagues who follow more familiar paths.
The challenge for leadership is recognizing those strengths and matching them with appropriate responsibilities.
That doesn't mean every neurodivergent employee has the same abilities or should be assigned the same work. It means organizations should evaluate what individuals actually do well rather than expecting everyone to demonstrate competence in identical ways.
Sachs makes a broader point: Cognitive diversity should be treated as an element of security control effectiveness, not simply a workforce accommodation or cultural initiative.
If an organization discourages unconventional thinkers, direct communicators or employees who question assumptions, it may be filtering out valuable security information.
And in an industry where missed signals can have enormous consequences, that becomes an operational risk.
Cybersecurity hiring may be screening out the wrong people
Copeland also challenges how organizations recruit cybersecurity professionals.
Job descriptions frequently contain requirements disconnected from the actual responsibilities of the position. Degrees, certifications and years of experience become screening mechanisms without sufficient consideration of whether those qualifications predict job performance.
He questions the practice of assembling job descriptions from existing postings without evaluating what the organization actually needs.
The result can be a hiring process that excludes capable candidates before they have an opportunity to demonstrate their abilities.
Copeland doesn't dismiss formal education. He acknowledges that completing a degree can demonstrate planning, persistence and an ability to work through challenges.
But those qualities don't automatically establish that someone will be an effective cybersecurity operator.
For security leaders already struggling with workforce shortages and skills gaps, the implication is significant.
Hiring for credentials and professional conformity may be easier to standardize. Hiring for the ability to solve real problems requires more careful evaluation.
Organizations need to distinguish between qualifications that are genuinely necessary and requirements that merely reflect conventional expectations of what a cybersecurity professional should look like.
Security policies need to account for real people
The conversation closes with another challenge to conventional cybersecurity leadership: the tendency to write policies without fully considering their consequences.
Asked where the industry needs to slow down and think more carefully, Copeland identifies policy development.
His example involves a seemingly reasonable restriction on smart glasses in the workplace.
From a security perspective, prohibiting devices capable of recording sensitive information may make sense.
But what happens when an employee relies on prescription smart glasses and doesn't have another pair?
A straightforward security rule can suddenly create questions involving accessibility, employment obligations, cost and accommodation.
The policy may be easy to write. Implementing it responsibly is more complicated.
It's an example of the larger problem Sachs and Copeland explore throughout the episode: Security controls operate in environments shaped by human needs, behaviors and circumstances.
Policies that ignore those realities can create friction, undermine trust and produce consequences their authors never anticipated.
Effective governance requires understanding not only what a rule is intended to prevent, but also how it affects the people expected to follow it.
Stronger security requires room to challenge assumptions
The episode ultimately makes a case for a more demanding definition of cybersecurity discipline.
Strong teams need reliable asset inventories, effective access controls, clear procedures and the ability to execute consistently under pressure.
But they also need people willing to question whether those procedures are working.
They need analysts who investigate anomalies others dismiss, employees who identify loopholes and leaders willing to hear uncomfortable conclusions.
That requires a culture in which disagreement isn't automatically interpreted as insubordination and different ways of thinking aren't treated as deficiencies.
Sachs and Copeland aren't arguing for less discipline. They're arguing for discipline that serves a purpose.
The distinction matters because cybersecurity failures don't always result from employees ignoring established procedures.
Sometimes they happen because everyone followed the same assumptions, trusted the same measurements and missed the same warning signs.
The goal isn't to build a cybersecurity team where everyone thinks alike. It's to build one where different thinkers can execute together — and recognize the threats that conformity might otherwise conceal.