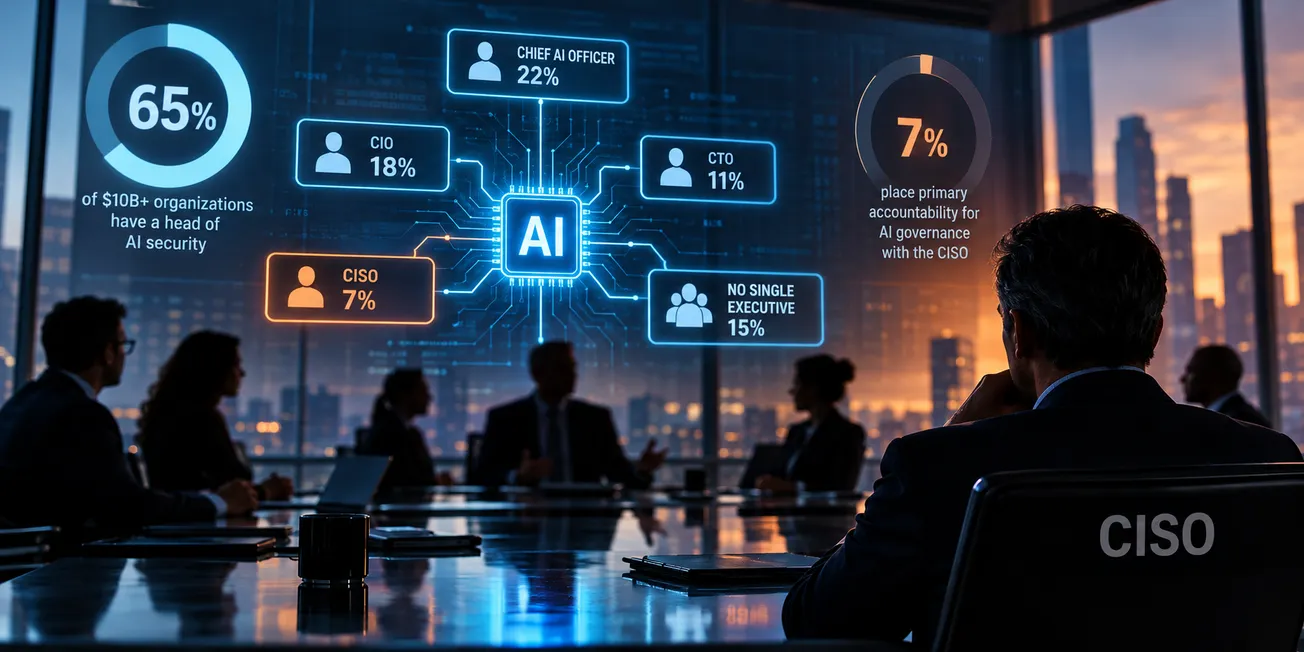
A new benchmark report from IANS and Artico Search finds that 65% of organizations with more than $10 billion in annual revenue have assigned a head of AI security, yet only 7% of those companies place primary accountability for enterprise AI governance with the CISO.
The 2026 Security Organizational Design Benchmark Report, released Oct. 20, draws on more than 1,400 responses from CISOs and cybersecurity staff collected between April and September, supplemented with staff-survey responses.
The report documents a rapid formalization of AI security leadership inside security organizations, concentrated at the largest companies: 18% of $10B-plus organizations have a dedicated head of AI security and another 47% have layered the responsibility onto another leadership role. Adoption drops sharply at smaller organizations: the role is dedicated at just 9% of $1B–$10B firms and 6% of under-$1B organizations, where it usually falls to existing GRC, SecOps, or architecture leads. Board oversight is lagging further behind: only 21% of $10B-plus enterprises have a fully implemented board committee for AI ethics or responsible AI, and 43% to 48% of organizations across all tiers have none planned.
At $10B-plus enterprises, AI governance accountability most often rests with a chief AI officer (22%), CIO (18%), or CTO (11%), while 15% report no single executive owns it. CISOs are more likely to hold it only at smaller firms—26% at under-$1B organizations versus 11% at $1B–$10B enterprises. The report also found that $10B-plus security organizations average 172 FTEs and a $90 million annual budget, and 58% now have a deputy CISO, though organizations usually run an external search rather than promote the deputy when the CISO leaves.
Building Enterprise-wide AI Governance
Building AI governance within enterprises has been a central storyline throughout 2026. Earlier this year, at the Ai4 AI conference, Krista Arndt, an associate CISO at St. Luke's University Health Network, described a two-stage, risk-based review for AI initiatives.
First, the health network considers whether a proposed use case actually makes sense for its business and culture, and how the agentic use case could affect patients. “Should we even do this, and does it make sense for our business model, our culture, and how it is going to impact our patients,” she said, are key questions that must be answered before being greenlit.
If it passes that assessment, it moves to a security and risk review, Arndt said. She also says governance can’t rely on policies and human behavior alone. Governance should be backed by technical controls that reduce risk in critical areas, with human oversight where appropriate.
The 2026 Security Organizational Design Benchmark Report found CISOs should map who currently owns enterprise AI governance and whether the security team has the scope and authority to cover AI risk. At $10B-plus organizations, they need to decide whether to create, combine, or defer a head of AI security role based on existing AppSec, data governance, identity, and GRC capabilities. If the board has no responsible-AI committee, that gap should be on the agenda before the next quarterly risk review, alongside a clear succession plan that addresses whether internal deputies are being evaluated against external board-ready candidates.
“The challenge for CISOs is determining how those capabilities come together around AI, where accountability belongs and whether the scope of the work has become significant enough to require dedicated leadership,” said Nick Kakolowski, senior research director at IANS. “The most difficult position for a CISO is to relitigate AI decisions made without security’s voice being heard,” said Steve Martano, IANS faculty and partner in Artico Search’s cyber practice.
The report leaves large-enterprise CISOs on the outside looking in: AI security roles are multiplying inside their organizations while accountability for AI governance remains outside their office.